1
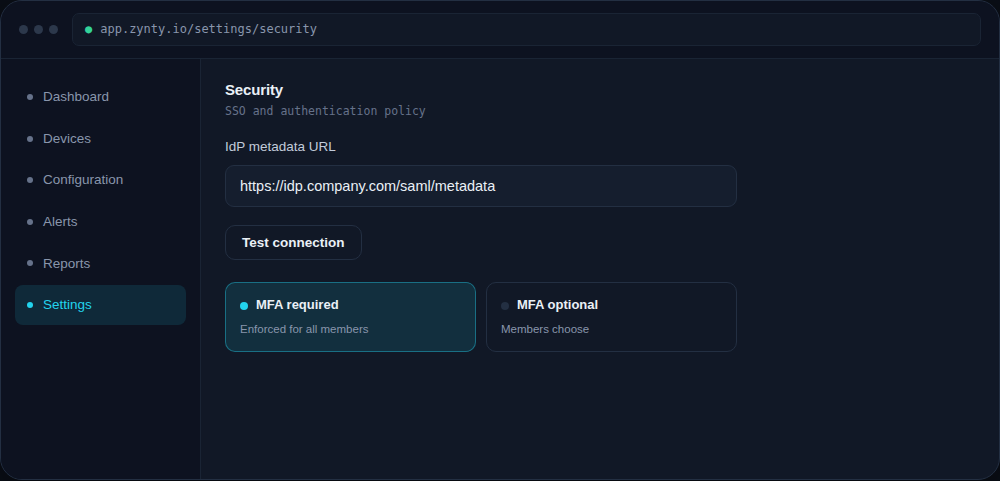
Enforce MFA and SSO from day one
Healthcare networks are high-value targets; require both single sign-on and multi-factor authentication rather than leaving either optional.
1
2
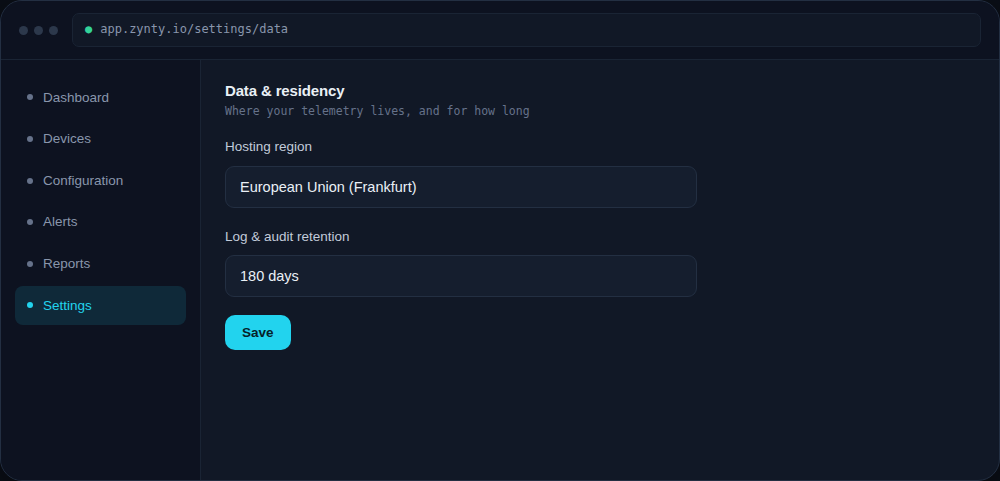
Set data residency and retention deliberately
Choose a hosting region and a retention period that match your organization's specific regulatory obligations, these vary by jurisdiction and aren't something a default setting can get right for you.
1
2
3
Segment monitoring the way your network is segmented
If clinical devices sit on an isolated VLAN, keep that isolation reflected in Zynty's groups and alert routing rather than flattening everything into one view.
4
Treat this as supporting evidence, not a compliance guarantee
Zynty's audit trail and access controls support the technical safeguards many healthcare regulations expect, but overall compliance depends on policy and process too, confirm specifics with your compliance officer.